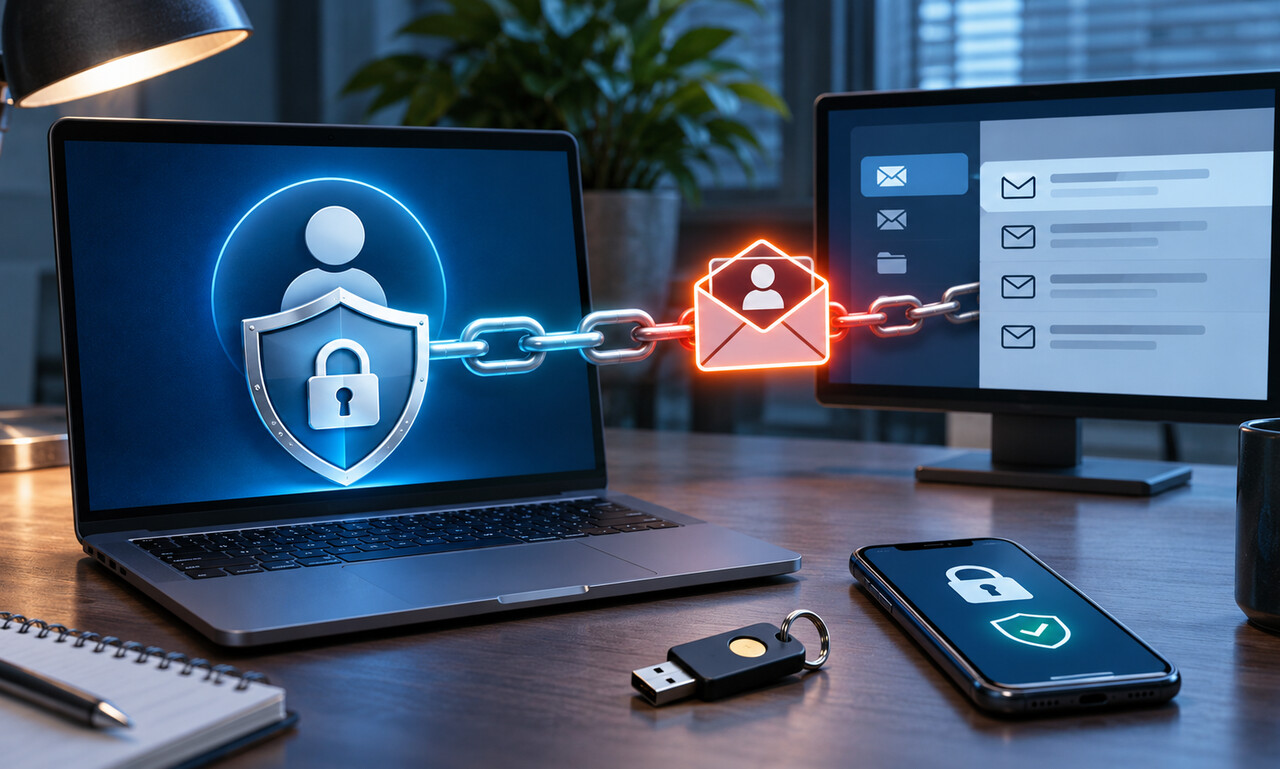
Recovery addresses are designed to help when a password is forgotten or a device is lost. Because they can receive reset links and security alerts, they may also provide a route around the stronger protections on the main account.
An old mailbox is especially risky if it uses a reused password, lacks a second factor or is rarely checked. An attacker who controls it may reset other services while deleting the warning messages before the owner notices.
Review recovery settings on important accounts and remove addresses you no longer use. Protect the remaining mailbox with a unique password, strong verification and updated recovery information of its own.
Avoid circular recovery chains in which two accounts depend only on each other. Store recovery codes separately and keep at least one trusted route that does not fail when a single provider or device becomes unavailable.
Security should be judged across the whole recovery path. The strongest sign-in method on the main account cannot compensate for an unlocked side door connected to it.
Original educational commentary by Breaking Click. This explainer is designed to help readers evaluate information more carefully.


